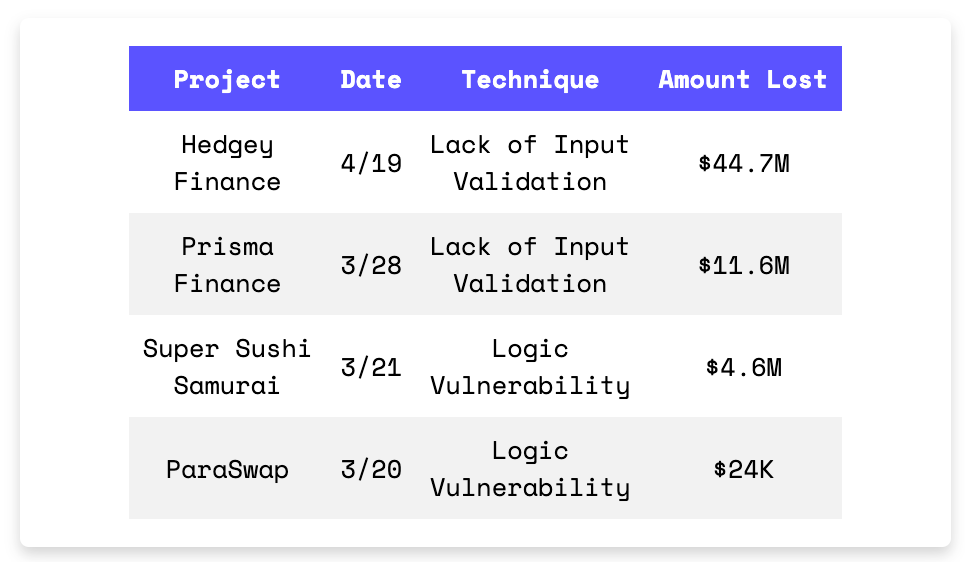
Hedgey Finance lost $44.7M due to lack of input validation.
Prisma Finance was targeted in a $11.6M attack.
Super Sushi Samurai was exploited for $4.6M.
Paraswap’s Augustus V6 contract was hacked for $24K.
Hacks
Hacks Analysis
Hedgey Finance | Amount Lost: $44.7M
On April 19th, the Hedgey Finance exploit on the Ethereum Mainnet resulted in a $44.7M loss. The root cause of the hack was the absence of proper input validation in the createLockedCampaign() function in Hedgey Finance’s ClaimCampaigns contract. The flaw enabled the attacker to execute arbitrary claimLockup parameters, invoking the createLockedCampaign() function and transferring approved tokens to their address. The Hedgey Finance team acknowledged the incident and sent an on-chain message to the exploiter.
On March 28th, the Prisma Finance exploit on the Ethereum Mainnet resulted in a $11.6M loss. The root cause of the hack was the absence of proper input validation in the MigrateTroveZap contract, specifically in the migrateTrove() function. This function, intended for automating trove manager migrations, miscalculated collateral and debt migration and triggered the debtToken::flashloan() function without proper input checks. This allowed the attacker to manipulate data and execute unauthorized trove migrations, exploiting delegated approvals to move assets to arbitrary addresses.
On March 21st, the Super Sushi Samurai exploit on the Blast Network resulted in a $4.6M loss. The root cause of the hack was a transfer logic flaw that allowed for an infinite mint scenario, where anyone could transfer tokens to themselves due to an oversight in the _update() function's implementation. This vulnerability resulted from the _balances[from] and _balances[to] values pointing to the same storage location when the from and to addresses were identical in a transfer operation. Consequently, each transfer call effectively doubled the token holdings of the caller.
Exploit Contract (on Blast Network): 0xdfdcdbc789b56f99b0d0692d14dbc61906d9deed
On March 20th, the ParaSwap exploit on the Ethereum Mainnet resulted in a $24K loss. The root cause of the hack was that the uniswapV3SwapCallback() function in the Uniswap V3 Pool of the AugustusV6 contracts enabled the attacker to redirect funds from authorized addresses to their controlled address. The ParaSwap team acknowledged the incident, paused all transactions, and sent on-chain messages to the exploiter.